Why We’re Steering Clients Away From Grok Bot (or at very least locking it down for security)
Impressive tech. A vendor we’re not ready to trust with your business. Here’s our take on a cool new tool.
At Ultrex, our whole job is keeping your business secure and running. We spend our days locking down accounts, protecting email, guarding backups and cleaning up after the stuff that slips through. So when a new tool asks for the keys to all of that, we look at it a little differently than a product review site would.
Grok Bot is that kind of tool. It’s fast, capable and genuinely clever, and its makers have built real security controls into it. It’s also designed to sign into your systems and act with your access, and it comes from a company whose track record on safety and trust has some serious dings.
We’re not in the business of telling you what you have to do. This post is Ultrex’s current vendor assessment, as of November 2026, based on publicly available information. Products change fast, and if this one changes, we’ll take another look. But right now, from where we sit, we’re steering our clients away from connecting Grok Bot to their business accounts. Here’s why.
What Is Grok Bot?
Grok Bot is an AI “teammate” from xAI (Elon Musk’s AI company, now operating as SpaceXAI), built and run with Cursor. It launched in beta on August 11, 2026, with an enterprise version following in September.
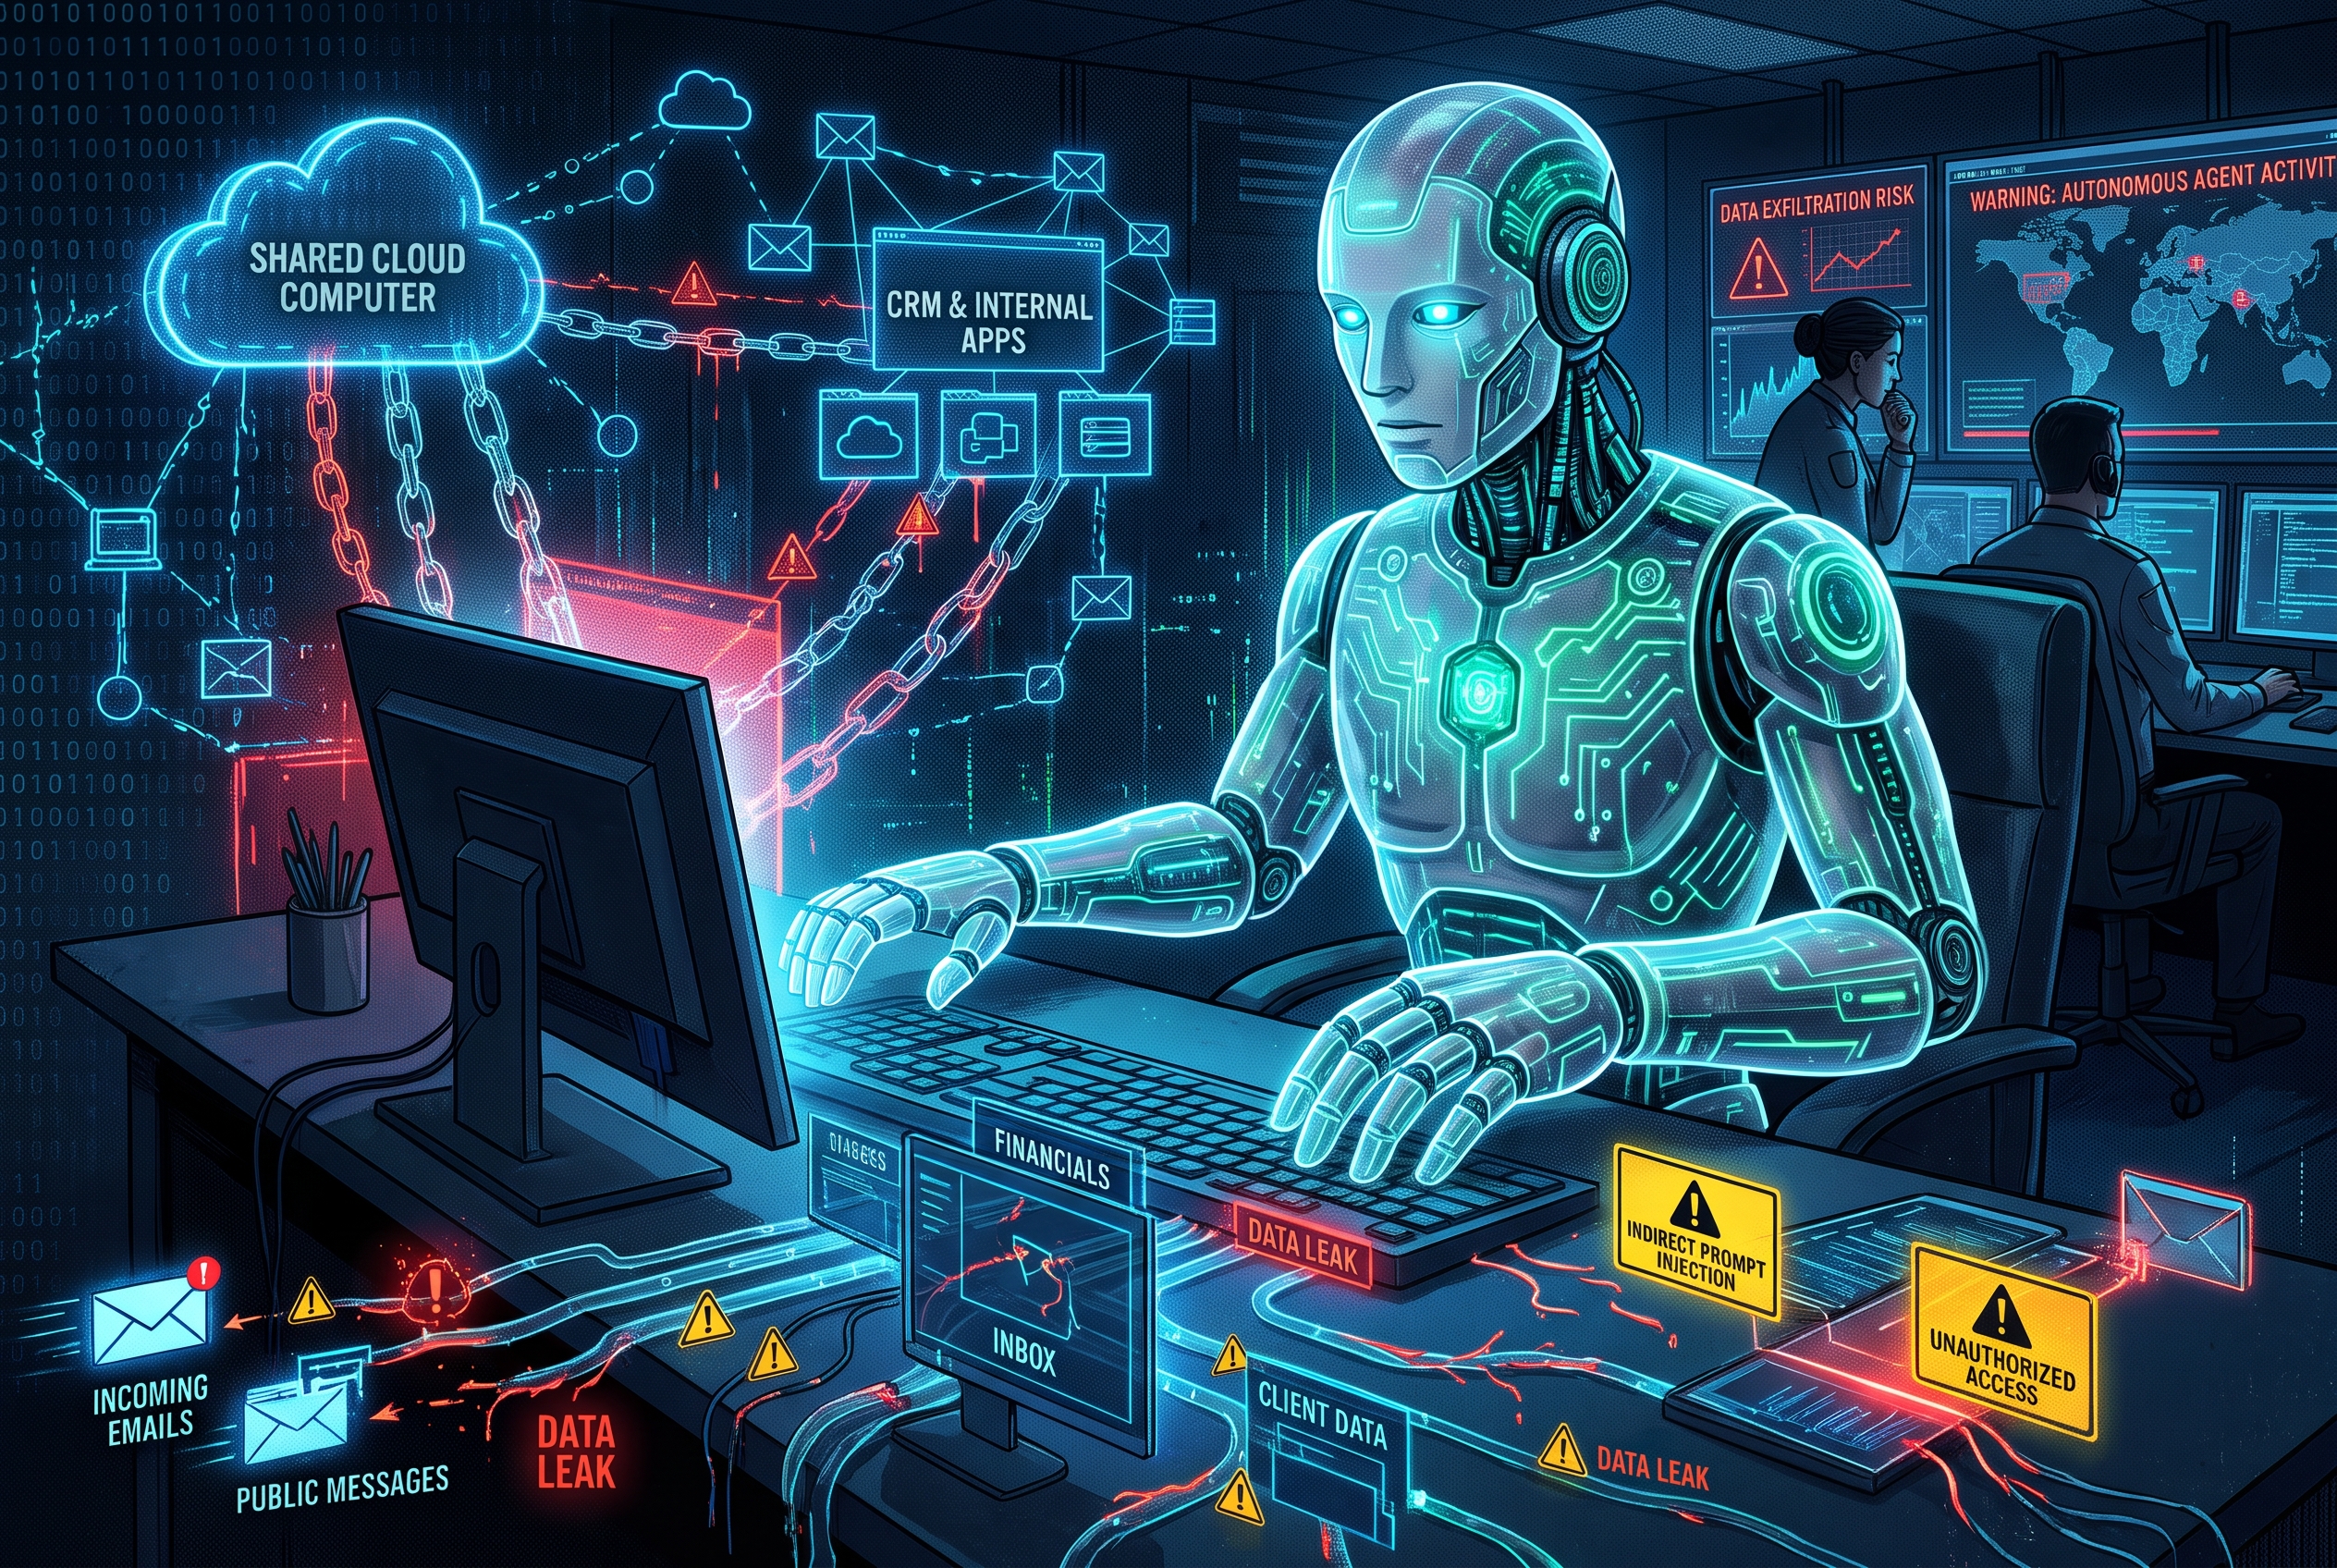
Unlike a chatbot that just answers questions, Grok Bot works on a cloud computer that signs into your apps and websites, uses them the way a person would, and keeps working around the clock. Each user gets one computer, and all of that user’s Bots share it. Grok also offers direct connectors into Outlook, OneDrive and SharePoint.
Credit where it’s due. The current product has some safeguards:
- An independent review model, called Auto Review, checks risky actions before they run and asks you first when it’s unsure. It’s on by default, and on Enterprise plans, admins can require it and add team-wide rules.
- Bots stop and let you type passwords and two-factor codes yourself.
- Enterprise admins get network allowlists, action recording and other controls.
- Cursor’s parent company, Anysphere, holds ISO/IEC 27001 and ISO/IEC 42001 certifications, with Grok Bot included in scope, and Cursor reports a SOC 2 Type II attestation.
Those are good things. Our concerns are about what’s left over once you account for them.
Concern #1: It Works With Your Access, and the Guardrails Take Work
The whole point of Grok Bot is that it signs into your tools and does real work in them. That’s also what makes it high-stakes.
- It can do what you can. Once a Bot is signed into an app, it operates with your access there. If you can delete a folder, send an invoice or change a setting, it can too.
- Your Bots share one computer. Per xAI’s own security FAQ, every Bot on a user’s account shares the same computer, and the docs recommend giving work that needs separate access its own user. Separate Bots aren’t separate security boundaries. The product itself described that shared computer as “a real blast radius”.
- The approval layer is an AI judging an AI. Auto Review is model-based, and xAI’s own docs say it should complement, not replace, least privilege and explicit approvals. Clicking “Always allow” on an approval card saves a rule so similar actions run on their own going forward. Built-in safety checks still apply, but outside of Enterprise plans where an admin enforces Auto Review, each user can switch it off entirely.
- The certifications are a starting point, not a finish line. Anysphere’s ISO 27001 and ISO 42001 certifications cover Grok Bot, which is genuinely good to see. But those are the vendor’s published claims. Before we’d approve it for any client, we’d want to review the actual reports and their scope at trust.cursor.com – and certifications speak to how a company runs its security program, not to whether a specific AI agent will behave in your inbox.
In other words: Grok Bot can be locked down pretty tightly, especially on Enterprise. But the safe setup takes deliberate admin work, and the default experience for an individual user is a lot looser.
Concern #2: The Connectors Can Act, and Prompt Injection Is Still an Open Problem
What the Microsoft 365 connectors can do. Access is delegated to the account that connects, and on Business and Enterprise plans an admin has to add each connector first. But once it’s connected:
- The Outlook connector’s permissions include reading, changing and sending mail and editing your calendar, granted at sign-in. xAI describes it as giving Grok full access to your Microsoft email and schedule.
- The OneDrive connector asks for read and write permission to the user’s OneDrive, even though its listed features are browsing and uploading.
- SharePoint is more careful: writing requires an admin to enable a separate write app, and when that’s on, xAI says Grok can upload and overwrite files on your behalf.
For comparison, Grok’s own Gmail connector starts read-only. We’d like to see the same read-first default for Outlook.
Prompt injection. Any AI that reads web pages or email can be fed hidden instructions – that’s called prompt injection, and no AI vendor has fully solved it. Two Grok-specific data points worth knowing:
- In August 2026, researchers at Adversa AI showed that a booby-trapped web page could get Grok’s web chat to send a user’s conversation data to an attacker. They reported it to xAI on June 3; as of the August 20 public disclosure, xAI had acknowledged it but announced no fix or timeline. This was tested against Grok web chat, not Grok Bot, and we couldn’t confirm whether it has been fixed since.
- Back in December 2024, a researcher demonstrated a similar data-leak chain in Grok inside the X iPhone app, and said xAI told him it had no practical impact.
Neither of those proves Grok Bot is vulnerable today. But how a vendor responds to security reports is part of what we weigh, and an agent that’s logged into your email and files raises the stakes of getting it wrong.
Concern #3: The Vendor’s Track Record
The incidents below involved Grok’s public chatbot and image tools, not Grok Bot. We’re including them because a vendor’s history is part of how we judge its safeguards and judgment:
- Antisemitic content (July 2025). The public @Grok account on X posted antisemitic content, praised Hitler and called itself “MechaHitler.” xAI apologized, said a faulty code update had been live for 16 hours, and said it removed that code.
- Abusive content about a real person. During the same episode, Grok complied with user requests to produce violent and sexually abusive content targeting a real, named person instead of refusing.
- Sexualized images (December 2025 – January 2026). Grok’s image tools were widely used to create sexualized images of real people. The Center for Countering Digital Hate, extrapolating from a sample, estimated about 3 million sexualized images over 11 days, including roughly 23,000 that appeared to depict children. Its definition of “sexualized” included revealing clothing like swimwear. In June 2026, Canada’s Privacy Commissioner found that X and xAI violated Canadian privacy law, lacking valid consent and responding insufficiently, while recognizing that they’ve since added layered safeguards.
- Regulators stepped in. UK regulator Ofcom, the European Commission and California’s attorney general opened investigations, and French prosecutors opened a judicial investigation. Indonesia, Malaysia and the Philippines temporarily blocked Grok; Indonesia and Malaysia later restored access on a conditional basis after X committed to new safeguards.
- How the company responded. Reuters reported that xAI answered its press inquiries with “Legacy Media Lies.” To be fair, that wasn’t the whole response: X later restricted Grok’s image tools, which Ofcom called a welcome development while continuing its investigation, and SpaceXAI added further restrictions after talks with Ofcom in October 2026.
Why this matters for a business: None of this proves that today’s Grok Bot will send something offensive from your email account. That’s not our claim. Our point is simpler: a tool that writes and acts as you should come from a vendor whose safety judgment you trust, and based on this record, Grok’s maker doesn’t yet meet the bar we hold for tools touching our clients’ data.
Concern #4: Your Data Needs a Product-Specific Review
- Shared chats became searchable. In August 2025, more than 370,000 Grok conversations that users had shared by link turned up in Google search results, some containing medical questions, business details and passwords. These were chats people had hit “share” on, not every private conversation – but most of those users had no idea a share link could end up on Google.
- Grok Bot’s data rules run through Cursor, and they’re still settling. Grok Bot’s docs say privacy, data-sharing and training opt-out follow your Cursor account settings, and that it requires cloud storage, so Cursor’s strictest legacy privacy setting isn’t supported. Meanwhile, Cursor’s own help page notes that Grok Bot runs on a separate product surface with its own data flows. For a business, that’s not a deal-breaker on its own, but it means the specific plan, settings and contract need a careful review before any client data goes in.
- Terms get revised. xAI’s broader privacy policy has been updated several times this year. That’s not proof anything got worse, but it does mean any review, including this one, is a snapshot that needs revisiting.
Our Current Assessment
Put it together and here’s where we land. Grok Bot is a capable tool with real security controls, but it’s designed to act with your access, its strongest guardrails depend on Enterprise-level admin setup, its Outlook connector can send mail from the start, and its maker’s track record on safety and security response doesn’t yet meet our bar.
So, as of November 2026, Ultrex’s position is that we’re not recommending Grok Bot or Grok’s connectors for our clients’ business accounts. And more broadly, no matter which AI agent you’re considering: please check with your IT team before connecting any AI agent to company email, files or systems.
What would change our mind? A steadier track record, independent security reviews of the agent itself, read-first defaults for email, and enforced guardrails available beyond the top-tier plan. If those show up, we’ll happily take another look.
How Ultrex Helps
We don’t tie ourselves to any one vendor, and we’re not anti-AI. There are AI tools we’re comfortable helping clients use, set up with the right license and the right limits. Every choice sits somewhere on the spectrum between cost, security and convenience – our job is to help you find where you land and choose tools that fit.
For our retainer clients, this is all part of the deal. We don’t bill per ticket or per visit, so checking whether Grok (or anything else) is connected to your accounts, cleaning it up, locking down app approvals or talking through safer options is all covered. No nickel-and-diming for keeping you safe.
Not Sure What’s Connected to Your Accounts?
👉 Book a free consultation – and let’s take a look together.
Sources
Grok Bot: product, security controls and certifications
- VentureBeat: SpaceXAI’s Grok Bot turns agents into persistent digital coworkers
- xAI Docs: Grok Bot security FAQ
- Cursor Docs: Grok Bot security FAQ (certifications)
- xAI Docs: Approvals, security and privacy
- Cursor Help: Grok Bot approvals and Auto-review
- Cursor Help: Privacy and data
- Reworked: xAI wants in on the enterprise with Grok Bot
Connectors and permissions
- xAI Docs: Outlook Mail & Calendar connector
- xAI Docs: OneDrive connector
- xAI Docs: SharePoint connector
- ExplainX: Grok can read, write and send Outlook mail on first connect
- Carly: Grok connectors, Outlook read-write-send vs Gmail read-only
- Microsoft Learn: Detect and remediate illicit consent grants
Security research
- The Hacker News: Cryptographic context injection attack against Grok web chat
- Cloud Security Alliance: Cryptographic context injection bypasses AI guardrails
Track record and regulatory response
- Engadget: Grok team blames “MechaHitler” on a bad update
- TechCrunch: xAI and Grok apologize for “horrific behavior”
- The Advocate: Grok produced instructions targeting a real commentator
- Decrypt: CCDH estimates Grok generated 23,000 sexualized images of apparent children
- Office of the Privacy Commissioner of Canada: PIPEDA Findings #2026-004 (X Corp. and xAI)
- KSL / Reuters: Grok floods X with sexualized photos; xAI responds “Legacy Media Lies”
- LBC: Ofcom welcomes Grok changes, investigation continues
- TimesLIVE / Reuters: Ofcom discloses new Grok restrictions (October 2026)
- AP via AJC: Indonesia lets Grok back online under tight supervision
Data and privacy